Posts Tagged ‘routers’

Best Home Wi-Fi settings for Maximum Speed and Internet coverage in Europe

Tuesday, July 21st, 2026

best-home-wifi-settings-for-maximum-speed-and-internet-coverage-europe-simple-steps-to-improve-your-home-wifi-signal

A fast broadband subscription is only part of the equation to have excellent internet air connectivity configuration for a home / work Wi-Fi Internet Router.
Even if you pay for good stable gigabit fiber options connection, poor Wi-Fi configuration can reduce your real-world speeds by more than half which might make working with devices have annoying temporary slownesses or even disruptions, when exchanging data to internet.

Our modern homes are filled with smart TVs, streaming devices, gaming consoles, laptops, smartphones, and IoT devices – all competing to take over fastest and stablest connectivity to the wireless device bandwidth.
Thus optimizing Wi-Fi router connectivity settings is no longer optional but is kind oa  in year 2026.

This snall guide would covers most of the best practices for configuring a home Wi-Fi network for maximum speed, stability, and security across Europe.

1. Choose the Right Wi-Fi Standard

Your router determines the maximum performance of your wireless network.


Recommended standards:

  • Wi-Fi 6 (802.11ax): Best value for most homes
  • Wi-Fi 6E: Excellent if your devices support the new 6 GHz band
  • Wi-Fi 7: Future-proof and ideal for multi-gigabit internet connections

! Avoid, using older Wi-Fi 5 or Wi-Fi 4 equipment unless upgrading is not possible !

2. Use the Best Frequency Band

Modern routers typically broadcast multiple wireless bands.


2.4 GHz Advantages:

  • Longer range
  • Better wall penetration
  • Disadvantages:
  • Lower speeds
  • More interference
  • Congested in apartments


2.4GHz Ideal for:

  • Smart home devices
  • Printers
  • Cameras

5 GHz Advantages:


  • Higher throughput
  • Lower latency
  • Less interference
  • Ideal for:
  • Streaming
  • Gaming
  • Video conferencing
  • Workstations


6 GHz (Wi-Fi 6E / Wi-Fi 7) Advantages:


  • Extremely low interference
  • Highest available speeds
  • Very low latency


6Ghz Wifi is usual use is:

With most modern Devices, such as (IoT connected devices, Wifi Gaming PCs, High-performance laptops, For large files transfer), tech quipment that looking for best Internet connectivity via air.. 

3. Position Your Router Correctly

best-wifi-router-placement-location-position-your-wireless-router-correctly-for-optimial-internet-air-speed

Router placement has a greater impact than many people realize.

Best practices for Router Positioning:

  • Place the router near the center of your home.
  • Position it on a shelf or table rather than on the floor.
  • Avoid placing it inside cabinets.
  • Keep it away from large metal objects.
  • Maintain distance from microwaves and cordless phones.
  • Keep antennas vertical unless the manufacturer recommends otherwise.
  • In multi-story homes, position the router between floors whenever possible.

4. Select the Best Wireless Channel

Channel congestion is one of the biggest causes of slow Wi-Fi.

For Europe (European Union countries):

For 2.4 GHz Wifi;

Use signal spread only:

  • Channel 1
  • Channel 6
  • Channel 11


These channels minimize overlap.

For 5 GHz;


Enable automatic channel selection or manually choose a channel with low congestion using a Wi-Fi analyzer.

5. Use the Correct Channel Width

For 2.4 GHz WiFi


Use:
+ 20 MHz
Avoid:
– 40 MHz unless there are very few neighboring networks.

For 5 GHz

Recommended:
+ 80 MHz
+ Use 160 MHz only if:
+ Few neighboring networks exist
+ Your devices support it

For 6 GHz

Use:
160 MHz or wider when available.

6. Enable WPA3 Security


Best WPA3 selection:

WPA3-Personal


For older devices require Backwards compatibility (keep enabled):
WPA2/WPA3 Mixed Mode

Avoid:
– WEP
– WPA
– Open networks
– Strong security helps prevent unauthorized users from consuming bandwidth.


7. Separate IoT Devices in different network

Many smart home devices generate unnecessary wireless traffic.
Create seperate networks for:

  • Main networ
  • Guest network
  • IoT network

This improves performance and enhances security.

8. Enable OFDMA and MU-MIMO

Modern Wi-Fi 6 routers support technologies that improve efficiency.
OFDMA

Allows multiple devices to share wireless resources efficiently.
MU-MIMO
Enables simultaneous communication with multiple devices.

Both should remain enabled.

9. Update Router Firmware

Manufacturers regularly release updates that improve the Performance, Security, Stability, Compatibility.
As script kiddie "hackers" threaths raise seriously day by day, when possible always, do:

  • Enable automatic firmware updates whenever possible.

10. Use Quality of Service (QoS)


Use the router to QoS prioritizes important traffic
Usual candidates for higher priorty internet traffics configs are:

  • Streaming, Work VPN traffic
  • Gaming, Video calls


Se as Lower priority ones :

  • Downloads
  • Cloud automated backups, etc.

11. Disable Legacy Wi-Fi Modes


Older compatibility modes, has advantages for interoperability but does reduce network efficiency, so most people would like to disable it.

Disable wifi mode transmission:

– 802.11b
– 802.11g


For Performance use instead the newer transmissions:

+ 802.11n
+ 802.11ac
+ 802.11ax

12. Always Prefer Wired Connections for High-Bandwidth Devices

alwayes-prefer-wired-connections-for-high-bandwidth-devices-cable-network-connection-should-be-always-first-choice

Connect these devices via Ethernet whenever possible:

  • NAS systems (Storages), Desktop PCs (most important candidates for UTP connectivity)
  • Gaming consoles, Smart TVs, Streaming boxes (secondary but also important to not disrupt your fun time)


Note !:
 Every cable connected device would have possible impact on any other connected Wi-Fi devices such as Mobile phones.
Every wired device reduces wireless congestion!

13. Use Mesh Wi-Fi for large sized sq. meter homes

If your home exceeds approximately 150–200 m² or has multiple floors, consider a mesh Wi-Fi system instead of relying on a single router.


Benefits includes:

  • Better coverage
  • Seamless roaming
  • Higher overall speeds
  • Reduced dead zones

14. Monitor Network Usage


Many routers provide tools to identify bottlenecks. Some common ones are

  • Bandwidth-heavy devices, Weak connections


    Review these statistics as regular as possible to optimize your network and have decent internet connectivty.

  • Congested channels, Signal quality issues

15. Understand European Wi-Fi Regulations

European countries follow ETSI regulations for wireless spectrum.
Most routers sold in Europe automatically comply with regional requirements, including:

Permitted transmit power, DFS (Dynamic Frequency Selection), follow approved set wireless channels.

! Avoid changing the router's region setting, as this may violate local regulations and reduce compatibility. !

Example Configuration for a Modern European Home (Recommended Value Settings)
 

  1. Wi-Fi Standard    Wi-Fi 6 or newer
  2. Security    WPA3-Personal
  3. 2.4 GHz Channel    1, 6, or 11
  4. 2.4 GHz Width    20 MHz
  5. 5 GHz Width    80 MHz
  6. 6 GHz Width    160 MHz (if supported)
  7. Firmware    Automatic updates enabled
  8. QoS    Enabled
  9. OFDMA    Enabled
  10. MU-MIMO    Enabled
  11. Smart Connect    Enabled unless manual band control is preferred
  12. DNS    ISP, Cloudflare (1.1.1.1), or Google Public DNS (8.8.8.8)


Common mistakes to avoid


  • Placing the router inside a cabinet.
  • Using outdated firmware.
  • Running all devices on the 2.4 GHz band.
  • Selecting crowded wireless channels.
  • Leaving the default administrator password unchanged.
  • Using Wi-Fi extenders instead of a proper mesh system in large homes.
  • Connecting high-bandwidth devices wirelessly when Ethernet is available.

Conclusion

Optimizing a home Wi-Fi network involves more than purchasing a fast router. Proper placement, choosing the right frequency bands, selecting appropriate channels, keeping firmware updated, and enabling modern Wi-Fi features such as OFDMA and MU-MIMO can significantly improve speed, reliability, and coverage.
For most European households, a centrally located Wi-Fi 6 router configured with WPA3 security, 80 MHz channels on the 5 GHz band, and Ethernet connections for high-bandwidth devices provides an excellent balance of performance, security, and future readiness.
Linux Bond network interfaces to merge multiple interfaces ISPs traffic – Combine many interfaces NIC into one on Debian / Ubuntu / CentOS / Fedora / RHEL Linux

Tuesday, December 16th, 2014

how-to-create-bond-linux-agregated-network-interfaces-for-increased-network-thoroughput-debian-ubuntu-centos-fedora-rhel
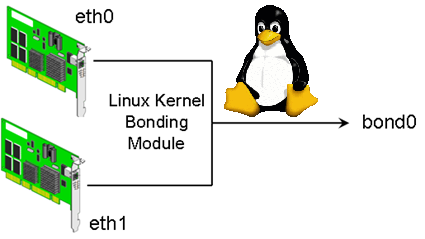
Bonding Network Traffic
 (link aggregation) or NIC teaming is used to increase connection thoroughput and as a way to provide redundancy for a services / applications in case of some of the network connection (eth interfaces) fail. Networking Bonding is mostly used in large computer network providers (ISPs), infrastructures, university labs or big  computer network accessible infrastructures or even by enthusiatst to run home-server assuring its >= ~99% connectivity to the internet by bonding few Internet Providers links into single Bonded Network interface. One of most common use of Link Aggreegation nowadays is of course in Cloud environments.  

 Boding Network Traffic is a must know and (daily use) skill for the sys-admin of both Small Company Office network environment up to the large Professional Distributed Computing networks, as novice GNU /  Linux sys-admins would probably have never heard it and sooner or later they will have to, I've created this article as a quick and dirty guide on configuring Linux bonding across most common used Linux distributions.

It is assumed that the server where you need network boding to be configured has at least 2 or more PCI Gigabyte NICs with hardware driver for Linux supporting Jumbo Frames and some relatively fresh up2date Debian Linux >=6.0.*, Ubuntu 10+ distro, CentOS 6.4, RHEL 5.1, SuSE etc.
 

1. Bond Network ethernet interfaces on Debian / Ubutnu and Deb based distributions

To make network bonding possible on Debian and derivatives you need to install support for it through ifenslave package (command).

apt-cache show ifenslave-2.6|grep -i descript -A 8
Description: Attach and detach slave interfaces to a bonding device
 This is a tool to attach and detach slave network interfaces to a bonding
 device. A bonding device will act like a normal Ethernet network device to
 the kernel, but will send out the packets via the slave devices using a simple
 round-robin scheduler. This allows for simple load-balancing, identical to
 "channel bonding" or "trunking" techniques used in switches.
 .
 The kernel must have support for bonding devices for ifenslave to be useful.
 This package supports 2.6.x kernels and the most recent 2.4.x kernels.


apt-get –yes install ifenslave-2.6


Bonding interface works by creating a "Virtual" network interface on a Linux kernel level, it sends and receives packages via special
slave devices using simple round-robin scheduler. This makes possible a very simple network load balancing also known as "channel bonding" and "trunking"
supported by all Intelligent network switches

Below is a text diagram showing tiny Linux office network router configured to bond ISPs interfaces for increased thoroughput:


Internet
 |                  204.58.3.10 (eth0)
ISP Router/Firewall 10.10.10.254 (eth1)
   
                              | -----+------ Server 1 (Debian FTP file server w/ eth0 & eth1) 10.10.10.1
      +------------------+ --- |
      | Gigabit Ethernet       |------+------ Server 2 (MySQL) 10.10.10.2
      | with Jumbo Frame       |
      +------------------+     |------+------ Server 3 (Apache Webserver) 10.10.10.3
                               |
                               |------+-----  Server 4 (Squid Proxy / Qmail SMTP / DHCP) 10.10.10.4
                               |
                               |------+-----  Server 5 (Nginx CDN static content Webserver) 10.10.10.5
                               |
                               |------+-----  WINDOWS Desktop PCs / Printers & Scanners, Other network devices 


Next to configure just installed ifenslave Bonding  
 

vim /etc/modprobe.d/bonding.conf

alias bond0 bonding
  options bonding mode=0 arp_interval=100 arp_ip_target=10.10.10.254, 10.10.10.2, 10.10.10.3, 10.10.10.4, 10.10.10.5


Where:

  1. mode=0 : Set the bonding policies to balance-rr (round robin). This is default mode, provides load balancing and fault tolerance.
  2. arp_interval=100 : Set the ARP link monitoring frequency to 100 milliseconds. Without option you will get various warning when start bond0 via /etc/network/interfaces
  3. arp_ip_target=10.10.10.254, 10.10.10.2, … : Use the 10.10.10.254 (router ip) and 10.10.10.2-5 IP addresses to use as ARP monitoring peers when arp_interval is > 0. This is used determine the health of the link to the targets. Multiple IP addresses must be separated by a comma. At least one IP address must be given (usually I set it to router IP) for ARP monitoring to function. The maximum number of targets that can be specified is 16.

Next to make bonding work its necessery to load the bonding kernel module:

modprobe -v bonding mode=0 arp_interval=100 arp_ip_target=10.10.10.254, 10.10.10.2, 10.10.10.3, 10.10.10.4, 10.10.10.5


Loading the bonding module should spit some good output in /var/log/messages (check it out with tail -f /var/log/messages)

Now to make bonding active it is necessery to reload networking (this is extremely risky if you don't have some way of Console Web Java / VPN Access such as IPKVM / ILO / IDRAC), so reloading the network be absolutely sure to either do it through a cronjob which will automatically do the network restart with new settings and revert back to old configuration whether network is inaccessible or assure physical access to the server console if the server is at your disposal.

Whatever the case make sure you backup:

 cp /etc/network/interfaces /etc/network/interfaces.bak

vim /etc/network/interfaces

############ WARNING ####################
# You do not need an "iface eth0" nor an "iface eth1" stanza.
# Setup IP address / netmask / gateway as per your requirements.
#######################################
auto lo
iface lo inet loopback
 
# The primary network interface
auto bond0
iface bond0 inet static
    address 10.10.10.1
    netmask 255.255.255.0
    network 192.168.1.0
    gateway 10.10.10.254
    slaves eth0 eth1
    # jumbo frame support
    mtu 9000
    # Load balancing and fault tolerance
    bond-mode balance-rr
    bond-miimon 100
    bond-downdelay 200
    bond-updelay 200
    dns-nameservers 10.10.10.254
    dns-search nixcraft.net.in


As you can see from config there are some bond specific configuration variables that can be tuned, they can have positive / negative impact in some cases on network thoroughput. As you can see bonding interfaces has slaves (this are all other ethXX) interfaces. Bonded traffic will be available via one single interface, such configuration is great for webhosting providers with multiple hosted sites as usually hosting thousand websites on the same server or one single big news site requires a lot of bandwidth and of course requires a redundancy of data (guarantee it is up if possible 7/24h.

Here is what of configs stand for

 
  • mtu 9000 : Set MTU size to 9000. This is related to Jumbo Frames.
  • bond-mode balance-rr : Set bounding mode profiles to "Load balancing and fault tolerance". See below for more information.
  • bond-miimon 100 : Set the MII link monitoring frequency to 100 milliseconds. This determines how often the link state of each slave is inspected for link failures.
  • bond-downdelay 200 : Set the time, t0 200 milliseconds, to wait before disabling a slave after a link failure has been detected. This option is only valid for the bond-miimon.
  • bond-updelay 200 : Set the time, to 200 milliseconds, to wait before enabling a slave after a link recovery has been detected. This option is only valid for the bond-miimon.
  • dns-nameservers 192.168.1.254 : Use 192.168.1.254 as dns server.
  • dns-search nixcraft.net.in : Use nixcraft.net.in as default host-name lookup (optional).

To get the best network thorougput you might want to play with different bounding policies. To learn more and get the list of all bounding policies check out Linux ethernet Bounding driver howto

To make the new bounding active restart network:
 

/etc/init.d/networking stop
sleep 5;
/etc/init.d/networking start


2. Fedora / CentOS RHEL Linux network Bond 

Configuring eth0, eth1, eth2 into single bond0 NIC network virtual device is with few easy steps:

a) Create following bond0 configuration file:
 

vim /etc/sysconfig/network-scripts/ifcfg-bond0


DEVICE=bond0
IPADDR=10.10.10.20
NETWORK=10.10.10.0
NETMASK=255.255.255.0
GATEWAY=10.10.10.1
USERCTL=no
BOOTPROTO=none
ONBOOT=yes


b) Modify ifcfg-eth0 and ifcfg-eth0 files /etc/sysconfig/network-scripts/

– Edit ifcfg-eth0

vim /etc/sysconfig/network-scripts/ifcfg-eth0

DEVICE=eth0
USERCTL=no
ONBOOT=yes
MASTER=bond0
SLAVE=yes
BOOTPROTO=none

– Edit ifcfg-eth1

vim /etc/sysconfig/network-scripts/ifcfg-eth1

DEVICE=eth0
USERCTL=no
ONBOOT=yes
MASTER=bond0
SLAVE=yes
BOOTPROTO=none


c) Load bond driver through modprobe.conf

vim /etc/modprobe.conf

alias bond0 bonding
options bond0 mode=balance-alb miimon=100


Manually load the bonding kernel driver to make it affective without server reboot:
 

modprobe bonding

d) Restart networking to load just configured bonding 
 

service network restart


3. Testing Bond Success / Fail status

Periodically if you have to administrate a bonded interface Linux server it is useful to check Bonds Link Status:

cat /proc/net/bonding/bond0
 

Ethernet Channel Bonding Driver: v3.5.0 (November 4, 2008)

Bonding Mode: fault-tolerance (active-backup)
Primary Slave: None
Currently Active Slave: eth0
MII Status: up
MII Polling Interval (ms): 100
Up Delay (ms): 0
Down Delay (ms): 0

Slave Interface: eth0
MII Status: up
Link Failure Count: 0
Permanent HW addr: 00:1e:0b:d6:6c:8f

Slave Interface: eth1
MII Status: up
Link Failure Count: 0
Permanent HW addr: 00:1e:0b:d6:6c:8c

To check out which interfaces are bonded you can either use (on older Linux kernels)
 

/sbin/ifconfig -a


If ifconfig is not returning IP addresses / interfaces of teamed up eths, to check NICs / IPs:

/bin/ip a show
1: lo: <LOOPBACK,UP,LOWER_UP> mtu 16436 qdisc noqueue state UNKNOWN
    link/loopback 00:00:00:00:00:00 brd 00:00:00:00:00:00
    inet 127.0.0.1/8 brd 127.255.255.255 scope host lo
    inet 127.0.0.2/8 brd 127.255.255.255 scope host secondary lo
    inet6 ::1/128 scope host
       valid_lft forever preferred_lft forever
2: eth0: <BROADCAST,MULTICAST,SLAVE,UP,LOWER_UP> mtu 1500 qdisc mq master bond0 state UP qlen 1000
    link/ether 00:1e:0b:d6:6c:8c brd ff:ff:ff:ff:ff:ff
3: eth1: <BROADCAST,MULTICAST,SLAVE,UP,LOWER_UP> mtu 1500 qdisc mq master bond0 state UP qlen 1000
    link/ether 00:1e:0b:d6:6c:8c brd ff:ff:ff:ff:ff:ff
7: bond0: <BROADCAST,MULTICAST,MASTER,UP,LOWER_UP> mtu 1500 qdisc noqueue state UP
    link/ether 00:1e:0b:d6:6c:8c brd ff:ff:ff:ff:ff:ff
    inet 10.239.15.173/27 brd 10.239.15.191 scope global bond0
    inet 10.239.15.181/27 brd 10.239.15.191 scope global secondary bond0:7156web
    inet6 fe80::21e:bff:fed6:6c8c/64 scope link
       valid_lft forever preferred_lft forever


In case of Bonding interface failure you will get output like:

Ethernet Channel Bonding Driver: v3.5.0 (November 4, 2008)
Bonding Mode: load balancing (round-robin)
MII Status: up
MII Polling Interval (ms): 100
Up Delay (ms): 200
Down Delay (ms): 200
Slave Interface: eth0
MII Status: up
Link Failure Count: 0
Permanent HW addr: 00:xx:yy:zz:tt:31
Slave Interface: eth1
MII Status: down
Link Failure Count: 1
Permanent HW addr: 00:xx:yy:zz:tt:30

Failure to start / stop bonding is also logged in /var/log/messages so its a good idea to check there too once launched:
 

tail -f /var/log/messages
Dec  15 07:18:15 nas01 kernel: [ 6271.468218] e1000e: eth1 NIC Link is Down
Dec 15 07:18:15 nas01 kernel: [ 6271.548027] bonding: bond0: link status down for interface eth1, disabling it in 200 ms.
Dec  15 07:18:15 nas01 kernel: [ 6271.748018] bonding: bond0: link status definitely down for interface eth1, disabling it

On bond failure you will get smthing like:

Dec  15 04:19:15 micah01 kernel: [ 6271.468218] e1000e: eth1 NIC Link is Down
Dec  15 04:19:15 micah01 kernel: [ 6271.548027] bonding: bond0: link status down for interface eth1, disabling it in 200 ms.
Dec  15 04:19:15 micah01 kernel: [ 6271.748018] bonding: bond0: link status definitely down for interface eth1, disabling it


4. Adding removing interfaces to the bond interactively
 

You can set the mode through sysfs virtual filesystem with:

echo active-backup > /sys/class/net/bond0/bonding/mode

If you want to try adding an ethernet interface to the bond, type:

echo +ethN > /sys/class/net/bond0/bonding/slaves

To remove an interface type:

echo -ethN > /sys/class/net/bond0/bonding/slaves


In case if you're wondering how many bonding devices you can have, well the "sky is the limit" you can have, it is only limited by the number of NIC cards Linux kernel / distro support and ofcourse how many physical NIC slots are on your server.

To monitor (in real time) adding  / removal of new ifaces to the bond use:
 

watch -n 1 ‘cat /proc/net.bonding/bond0′


How to harden Linux Security and imprpove network efficiency on Kernel sysctl Level to Stop SYN flood

Friday, July 8th, 2011

Power up Linux and protect against DDoS with sysctl var optimization

Some long time ago I’ve written an article Optimizing Linux tcp/ip networking

In the article I’ve examined a number of Linux kernel sysctl variables, which significantly improve the way TCP/IP networking is handled by a non router Linux based servers.

As the time progresses I’ve been continuing to read materials on blogs and internet sites on various tips and anti Denial of Service rules which one could apply on newly installed hosting (Apache/MySql/Qmail/Proxy) server to improve webserver responce times and tighten the overall security level.

In my quest for sysctl 😉 I found a few more handy sysctl variables apart from the old ones I incorporate on every Linux server I adminstrate.
The sysctl variables improves the overall network handling efficiency and protects about common SYN/ACK Denial of service attacks.

Here are the extra sysctl variables I started incorporating just recently:

############ IPv4 Sysctl Settings ################
#Enable ExecShield protection (randomize virtual assigned space to protect against many exploits)
kernel.randomize_va_space = 1
#Increase the number of PIDs processes could assign this is very needed especially on more powerful servers
kernel.pid_max = 65536
# Prevent against the common 'syn flood attack'
net.ipv4.tcp_syncookies = 1
# Controls the use of TCP syncookies two is generally a better idea, though you might experiment
#net.ipv4.tcp_syncookies = 1
net.ipv4.tcp_synack_retries = 2
##################################################
#
############## IPv6 Sysctl Settings ################
# Number of Router Solicitations to send until assuming no routers are present.
net.ipv6.conf.default.router_solicitations = 0
# Accept Router Preference in RA? Again not necessery if the server is not a router
net.ipv6.conf.default.accept_ra_rtr_pref = 0
# Learn Prefix Information in Router Advertisement (Unnecessery) for non-routers
net.ipv6.conf.default.accept_ra_pinfo = 0
# disable accept of hop limit settings from other routers (could be used for DoS)
net.ipv6.conf.default.accept_ra_defrtr = 0
# disable ipv6 global unicasts server assignments
net.ipv6.conf.default.autoconf = 0
# neighbor solicitations to send out per address (better if disabled)
net.ipv6.conf.default.dad_transmits = 0
# disable assigning more than 1 address per network interface
net.ipv6.conf.default.max_addresses = 1
#####################################################


To use this settings paste the above sysctl variables in /etc/sysctl.conf and ask sysctl command to read and apply the newly added conf settings:

server:~# sysctl -p
...

Hopefully you should not get errors while applying the sysctl settings, if you get some errors, it’s possible some of the variable is differently named (depending on the Linux kernel version) or the Linux distribution on which sysctl’s are implemented.

For some convenience I’ve created unified sysctl variables /etc/sysct.conf containing the newly variables I started implementing to servers with the ones I already exlpained in my previous post Optimizing Linux TCP/IP Networking

Here is the optimized / hardened sysctl.conf file for download

I use this exact sysctl.conf these days on both Linux hosting / VPS / Mail servers etc. as well as on my personal notebook 😉

Here is also the the complete content of above’s sysctl.conf file, just in case if somebody wants to directly copy/paste it in his /etc/sysctl.conf

# Sysctl kernel variables to improve network performance and protect against common Denial of Service attacks
# It's possible that not all of the variables are working on all Linux distributions, test to make sure
# Some of the variables might need a slight modification to match server hardware, however in most cases it should be fine
# variables list compiled by hip0
### https://www.pc-freak.net
#### date 08.07.2011
############ IPv4 Sysctl Kernel Settings ################
net.ipv4.ip_forward = 0
# ( Turn off IP Forwarding )
net.ipv4.conf.default.rp_filter = 1
# ( Control Source route verification )
net.ipv4.conf.default.accept_redirects = 0
# ( Disable ICMP redirects )
net.ipv4.conf.all.accept_redirects = 0
# ( same as above )
net.ipv4.conf.default.accept_source_route = 0
# ( Disable IP source routing )
net.ipv4.conf.all.accept_source_route = 0
# ( - || - )net.ipv4.tcp_fin_timeout = 40
# ( Decrease FIN timeout ) - Useful on busy/high load server
net.ipv4.tcp_keepalive_time = 4000
# ( keepalive tcp timeout )
net.core.rmem_default = 786426
# Receive memory stack size ( a good idea to increase it if your server receives big files )
##net.ipv4.tcp_rmem = "4096 87380 4194304"
net.core.wmem_default = 8388608
#( Reserved Memory per connection )
net.core.wmem_max = 8388608
net.core.optmem_max = 40960
# ( maximum amount of option memory buffers )
# tcp reordering, increase max buckets, increase the amount of backlost
net.ipv4.tcp_max_tw_buckets = 360000
net.ipv4.tcp_reordering = 5
##net.core.hot_list_length = 256
net.core.netdev_max_backlog = 1024
#Enable ExecShield protection (randomize virtual assigned space to protect against many exploits)
kernel.randomize_va_space = 1
#Increase the number of PIDs processes could assign this is very needed especially on more powerful servers
kernel.pid_max = 65536
# Prevent against the common 'syn flood attack'net.ipv4.tcp_syncookies = 1
# Controls the use of TCP syncookies two is generally a better idea, though you might experiment
#net.ipv4.tcp_syncookies = 1
net.ipv4.tcp_synack_retries = 2
###################################################
############## IPv6 Sysctl Settings ################
# Number of Router Solicitations to send until assuming no routers are present.
net.ipv6.conf.default.router_solicitations = 0
# Accept Router Preference in RA? Again not necessery if the server is not a router
net.ipv6.conf.default.accept_ra_rtr_pref = 0
# Learn Prefix Information in Router Advertisement (Unnecessery) for non-routersnet.
ipv6.conf.default.accept_ra_pinfo = 0
# disable accept of hop limit settings from other routers (could be used for DoS)
net.ipv6.conf.default.accept_ra_defrtr = 0
# disable ipv6 global unicasts server assignmentsnet.
ipv6.conf.default.autoconf = 0
# neighbor solicitations to send out per address (better if disabled)
net.ipv6.conf.default.dad_transmits = 0
# disable assigning more than 1 address per network interfacenet.
ipv6.conf.default.max_addresses = 1
#####################################################
# Reboot if kernel panic
kernel.panic = 20

These sysctl settings will tweaken the Linux kernel default network settings performance and you will notice the improvements in website responsiveness immediately in some cases implementing this kernel level goodies will make the server perform better and the system load might decrease even 😉

This optimizations on a kernel level are not only handy for servers, their implementation on Linux Desktop should also have a positive influence on the way the network behaves and could improve significantly the responce times of opening pages in Firefox/Opera/Epiphany Torrent downloads etc.

Hope this kernel tweakenings are helpful to someone.
Cheers 😉

Selecting Best Wireless channel / Choosing Best Wi-FI channel for Wireless Routers or (How to improve Wireless Network performance)

Monday, February 22nd, 2010

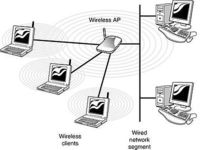
Wireless AP
Below are some valuable advices on Wireless Access Point initial install and configuration to better off your Wireless connection.It’s worthy to note that the 2.4 GHz

Wi-Fi signal range is divided into a number of smaller bands or “channels,” similar to television channels. I decided to run my wireless on channel 12 since this there was no other wireless routers operating on that frequency, though most routers are preconfigured to spread it’s signal on channel 6.

There is a difference in channels available for setup for 802.11b and 802.11g wireless networks in the United States and the European Union. In the USA the wireless channels available are from (1 to 11) whether in the EU it’s in the range of (1-13). Each of the Wireless channels run on a different frequency.

The lower the number of the channel is the lowest the radiating frequence band on which data is transmitted .Subsequently, increasing the channel increases the frequency slightly. Therefore the higher the channel you select on your AP the lesser the overlap with other devices running on the same channel and thus the lesser the possibility to overlap and interference.
It’s quite likely that you experience problems, if you use the default wireless channel which is 6.
If that’s the case it’s recommended to use either channel 1 or channel 11. In case of interference, i.e. overlap with other wireless networks, cellphones etc., there are 2 possible ways to approach the situation. In case of smaller interference, any change in channel on which there is no wireless device running could fix it up. The second way is to choose a wireless channel for your router in between 1,6 or 11 in (The USA) or 1,7,13 in Europe.
Up to 3 networks can run on the same space with minimum interference, therefore it would be a wise idea to check the list of wireless routers in your and check if there are others running on the same frequency.
As I mentioned in the beginning of the post I initially started running my wireless on channel 12, however after I discovered it is recommended to run your wireless router either on channel 1 7 or 13 in Europe I switched my D-Link DI-524 wireless router to transmit it’s signal on Channel 13.

I should testify that after changing the wireless channel, there was quite an improvement in my wireless connection.For instance before I change to Channel 13 (when my wireless internet was still streamed on channel 12) my wireless had constantly issues with disconnects because of low wireless signal.

Back then My wireless located physically in like 35 meters away set in another room, I can see my wireless router hardly connected on like 35%, changing to channel 13 enhanced my connection to the current 60% wireless router availability.

It’s also an interesting fact that Opened Wireless networks had better network thoroughput, so if you’re living in a house with a neighbors a bit distant from your place then you might consider it as a good idea to completely wipe out Wireless Router security encryption and abandon the use of WEP or WPA network encryption.

In case if all of the above is not working for you, you might consider take a close look at your Wireless Wireless LAN pc card and see if there are no any kind of bumps there. Another really interesting fact to know is that many people here in Bulgaria tend to configure there Wireless Access Points on channels either 1,6 or 11 which is quite inadequate considering that we’re in the EU and we should use a wireless channel between 1, 7 or 13 as prescribed for EU citizens.

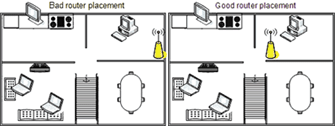
Another thing not to forget is to place your wireless in a good way and prevent it from interferences with other computer equipment. For example keep the router at least few meters away from PC equipment, printers, scanners, cellphones, microwaves. Also try to put your wireless router on some kind of central place in your home, if you want to have the wireless signal all around your place.

At my place I have a microwave in the Kitchen which is sometimes an obstacle for the Wireless signal to flow properly to my notebook, fortunately this kind of interference happens rare (only when the Microwove is used to warm-up food etc.).Upgrading 802.11b wireless card / router to a better one as 802.11g is a wise idea too. 802.11g are said to be like 5 times faster than 802.11b.

You can expect 802.11b wireless network to transfer maximum between 2-5 Mbp/s whether 802.11g is claimed to transfer at approximately (12 to 23 Mbp/s). If even though the above prescriptions there is no wireless signal at some remote place at your home, you might consider adding a wireless repeater or change the AP router antenna.

By default wireless Routers are designed to be omni-directional (in other terms they broadcast the wireless signal all around the place. Thus is quite unhandy if you intend to use your Wireless net only in certain room or location at your place. If that’s the case for you, you might consider upgrading to a hi-gain antenna that will focus the wireless signal to an exact direction. Let me close this article with a small diagram taken from the net which illustrates a good router placement that will enable you to have a wwireless connection all over your place.

improve wireless router placement diagram